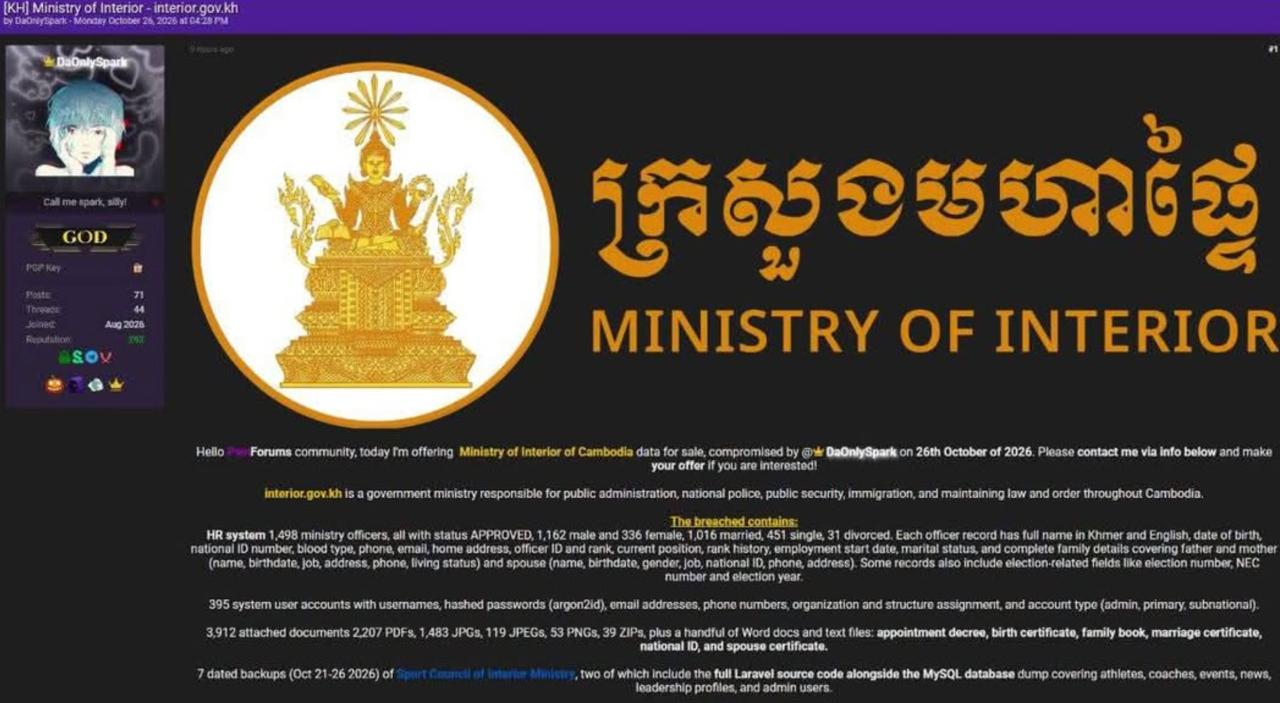
Reports recently emerged in the cybersecurity sector that a hacker using the alias “DaOnlySpark” exploited a remote code execution (RCE) vulnerability to breach the internal systems of several Cambodian institutions and allegedly leaked large quantities of sensitive files and databases. However, Cambodian authorities have not publicly confirmed the reported incidents as of now.
According to information circulating online, the Cambodia Digital Technology Institute (CADT) and the Digital Technology Research Institute may have leaked approximately 5.8GB of data, including source code, student and staff records, payment API credentials, system keys, and other sensitive information.
It was also reported that the Ministry of Interior data involved records of 1,498 officials, 395 system accounts, and 3,912 identity- and family-related documents; the Ministry of Commerce may also have suffered an internal network topology leak.
The National Employment Agency (NEA) was reportedly affected as well, with more than 25,000 applicant resumes, information on 8,185 companies, and 111 account records containing personal data potentially exposed.
If the reported information is accurate, the leaks could pose risks to personal privacy, institutional cybersecurity, and system operations. The authenticity of the incident, its precise scope, and whether the data have been misused remain subject to further verification by the authorities. The public should strengthen their cybersecurity awareness and avoid spreading or downloading purported leaked data from unknown sources.